
StackSafe builds supplier quality programs and provides supplier quality engineers to run them
What sets us apart?
We travel to suppliers, so you don’t have to. Your team is managing a million priorities, and the last thing you need is to pull resources away for supplier travel. That’s where we come in.
Industries We
Work With
Medical
Device
Class I, II, and III devices,
tissue banks, and more.
Services
Hourly consulting
Supplier Management & Quality, QA/RA, Kaizen Events
Internal & supplier audits
Engineering Led ISO 13485/9001, FDA QMSR
about us
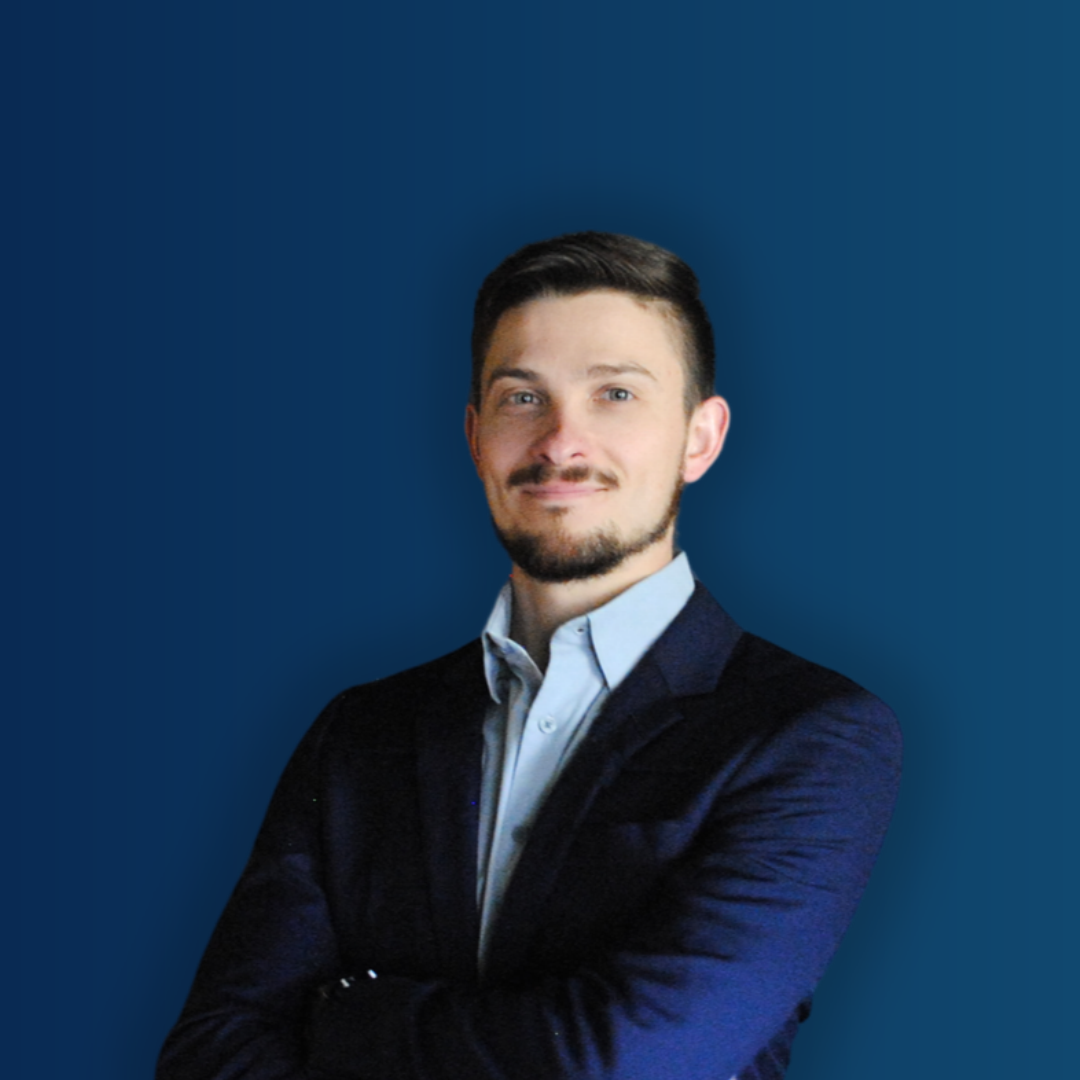
Greg Matson
Founder, StackSafe
Founded by Greg Matson, StackSafe specializes in MedTech auditing, supplier quality, and regulatory compliance, with over a decade of hands-on experience assessing suppliers for conformance, quality system maturity, and manufacturing capability.
He has supported organizations such as Boston Scientific, Outset Medical, UTC Aerospace, and General Dynamics in strengthening their QMS, improving supplier performance, and resolving complex compliance issues across MedTech, aerospace, defense, and advanced manufacturing.
ISO 13485 Lead Auditor
PECB Certified
MicroMaster’s, Supply Chain Management
MIT
AI Strategy and Governance Certificate
Wharton
Six Sigma Green Belt
IISE
B.S. Mechanical Engineering
North Dakota State University
Greg is a ComplianceQuest Partner
Add Subheading
Supplier Development: Turning Weak Suppliers into Strategic Partners

From Audit to Advantage: Evaluating Suppliers for Manufacturing Excellence
Managing Supplier Performance for Long-Term Improvement and Value
-
Internal audits evaluate your company’s own processes and QMS compliance, while supplier audits assess your vendors’ ability to meet product and possibly ISO 13485/9001 requirements. Both are essential for identifying risks and ensuring compliance.
-
ISO 13485/9001 and FDA QMSR require suppliers to be re-evaluated periodically, with frequency based on risk. Critical suppliers are often evaluated every 12 to 24 months, while lower-risk suppliers may be on a longer cycle. Perform a risk mapping exercise to determine supplier risk.
-
Independent auditors provide objectivity, technical expertise, and industry perspective. Engineering-led audits go beyond checklists- spotting gaps in design, operations, and compliance that internal teams may overlook.
-
Findings are documented in a report and categorized by non-conformity. You’ll need to develop a corrective action plan, track progress, and verify effectiveness to close the finding. After auditing, we can help develop and implement corrective actions, track progress, and verify effectiveness to fully close the findings.
frequently asked questions
Recommendations